
Snapshots are fast, cheap and built into AWS, so many teams treat them as backups. The problem is where they live. If someone takes over the account, they can delete the snapshots along with everything else.
Where snapshots fall short
- They usually sit in the same account and region as the data
- Anyone with enough permissions can delete them
- Retention is often managed by scripts that nobody tests
Turning snapshots into backups
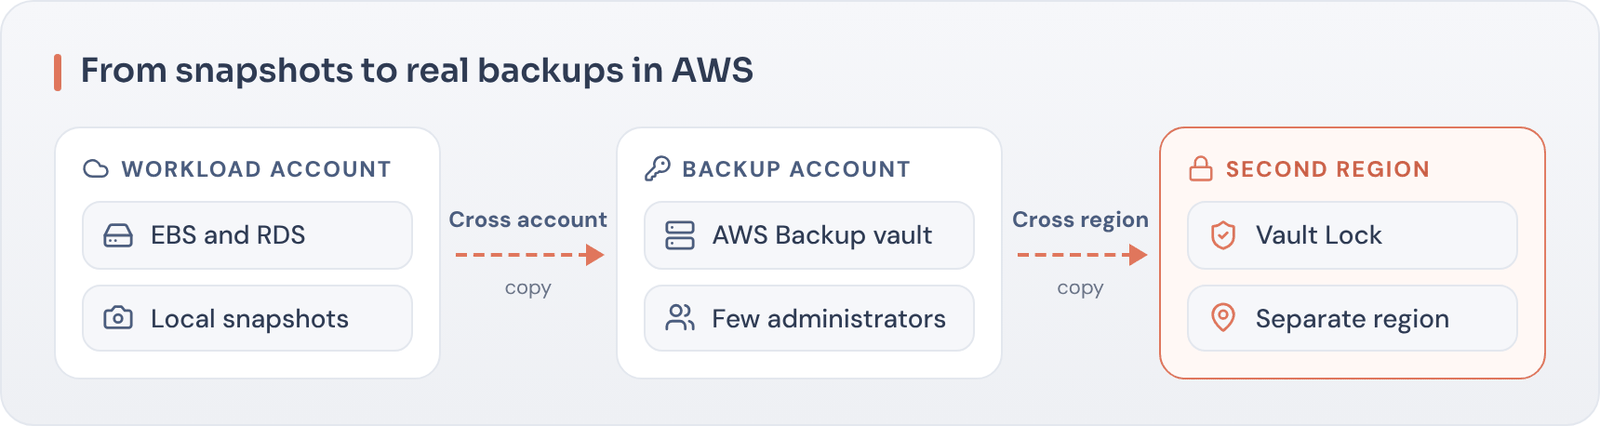
Use AWS Backup to manage policies across services. Copy recovery points to a separate account in your AWS Organization and to a second region. Apply Vault Lock in compliance mode to the vault that holds your most important copies so retention cannot be shortened.
Protect the backup account
The account that holds backups should have very few administrators, its own MFA protected access and service control policies that prevent deletion of vaults and recovery points.
Why it matters Cloud account takeover is a common way attackers destroy data. A separate, locked backup account is what lets you recover.
Key takeaways
- Snapshots in the same account are not backups.
- Copy to a separate account and region.
- Lock the vault and restrict who can administer it.
Would your AWS data survive an account takeover?
We review cloud backup architecture independently.