The EU Digital Operational Resilience Act (DORA) applies to financial entities and their critical ICT providers. It requires firms not just to plan for disruption, but to demonstrate they can withstand and recover from it.
Key themes
- ICT risk management with clear governance
- Incident management and reporting
- Digital operational resilience testing
- Management of ICT third-party risk
Implications for data protection
- Documented backup policies and recovery procedures
- Backups isolated from production systems
- Regular testing of backup and recovery
- Defined recovery-time and recovery-point objectives
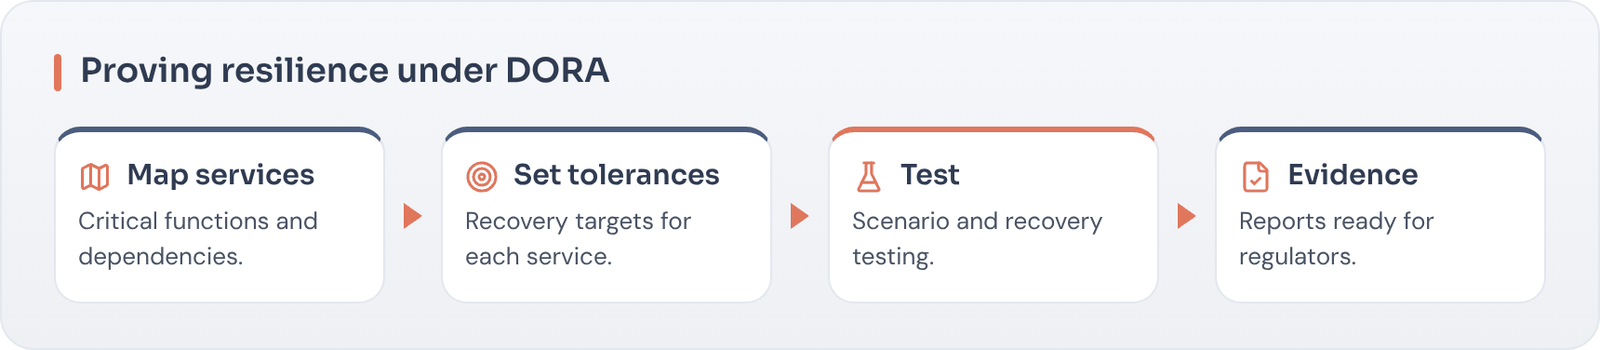
How to prepare
Map your current capabilities against the requirements, prioritize gaps and build a testing programme that produces evidence regulators can review.
Building a testing programme
DORA expects resilience testing proportionate to the size and risk profile of the firm. For data protection, that typically means regular backup restore tests, scenario-based recovery exercises and, for larger firms, more advanced testing of critical functions.
Each test should be planned, documented and followed by remediation of any findings. The test history itself becomes evidence of resilience for supervisors.
Key takeaways
- DORA requires demonstrable resilience, not just plans.
- Isolated backups and regular testing are central.
- Third-party providers are in scope too.
Preparing for regulatory scrutiny?
We provide independent validation of recovery capability aligned to regulatory frameworks.