The HIPAA Security Rule requires covered entities and business associates to have a contingency plan to protect electronic protected health information (ePHI) during emergencies, including cyberattacks.
Core elements
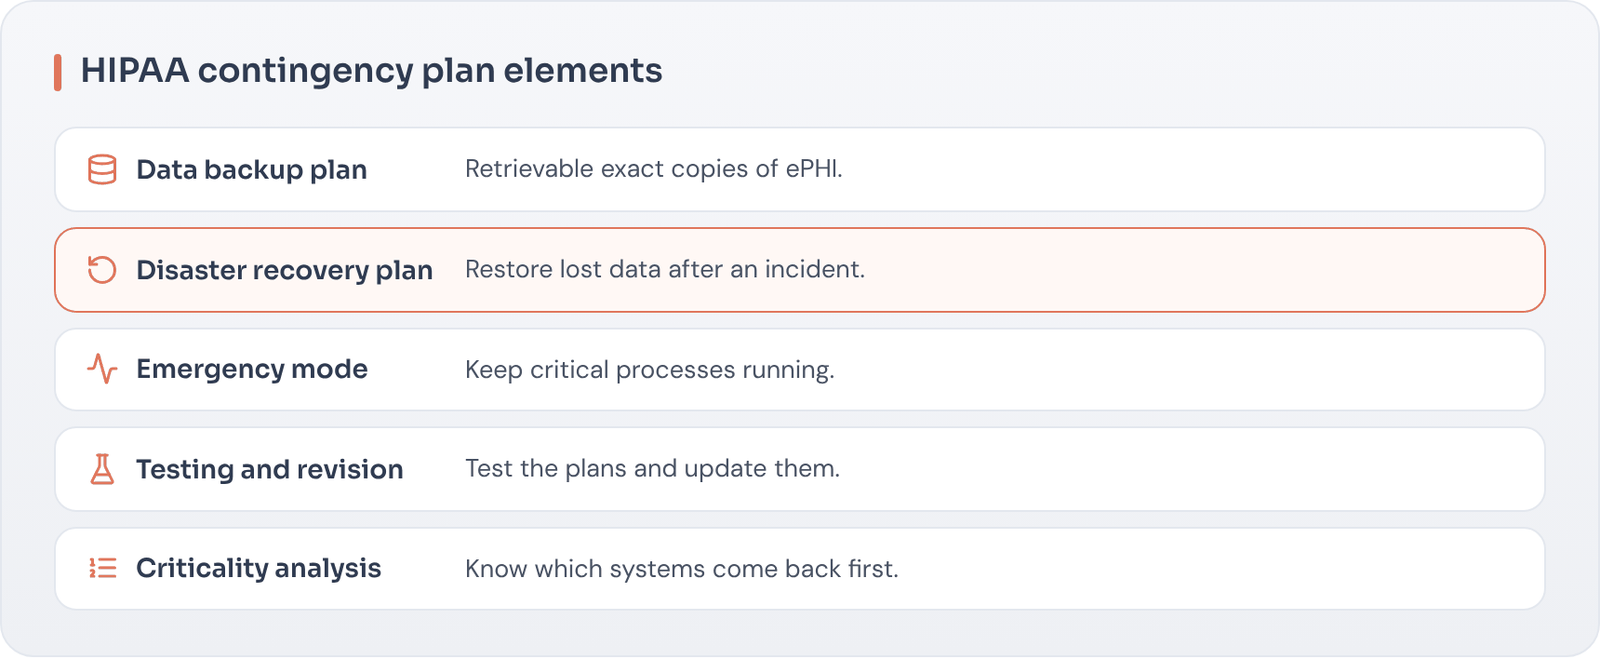
- Data backup plan: retrievable exact copies of ePHI.
- Disaster recovery plan: procedures to restore lost data.
- Emergency mode operation plan: protecting ePHI while operating in an emergency.
- Testing and revision and applications and data criticality analysis.
Why ransomware changes the picture
Healthcare is a frequent ransomware target. Backups that can be encrypted or deleted do not meet the intent of a reliable data backup plan.
Practical steps
- Identify systems that store or process ePHI.
- Protect backups with immutability and strong access control.
- Test restores and document the results.
- Review the plan after changes and incidents.
Common gaps we see in healthcare
- Backups of electronic health record systems that share credentials with production
- No documented emergency mode procedures for clinical operations
- Restore tests limited to individual files rather than full applications
- Business associates whose backup practices have not been assessed
Addressing these gaps strengthens both compliance and the practical ability to keep caring for patients during an incident.
Key takeaways
- HIPAA requires backup, DR and emergency-mode planning.
- Ransomware-resistant backups support compliance.
- Testing and documentation are expected.
Want an independent view of your recoverability?
Book a Recovery Readiness Call and we’ll help you turn assumptions into evidence.