
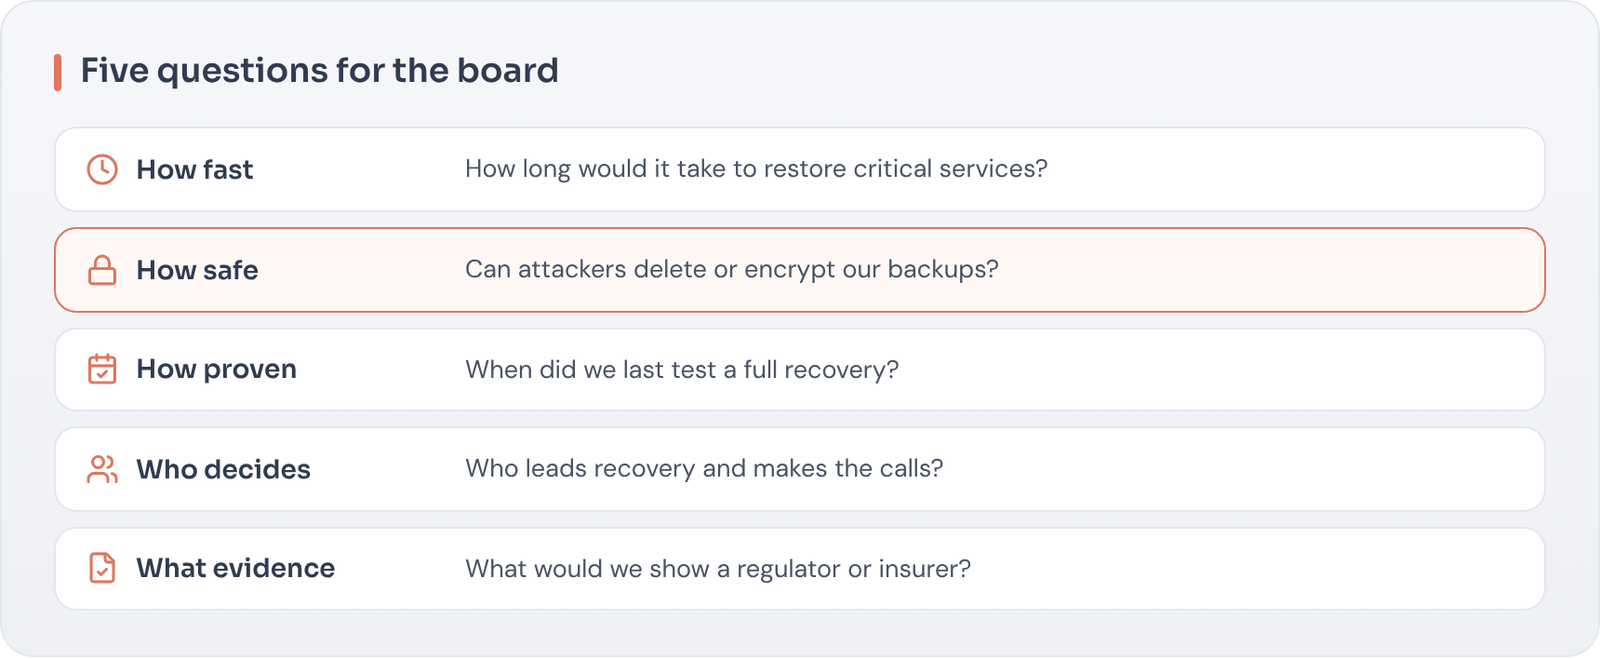
Cyber recovery is a business risk, not just an IT topic. These five questions help boards and executives understand whether the organization could recover from a serious attack.
The questions
- Which business services are most critical, and how long can we be without them?
- Do we have a copy of critical data that attackers cannot change or reach?
- When did we last prove we can recover: and what did we learn?
- Who decides, and how, during a major incident?
- Has an independent party validated our recovery capability?
What good answers sound like
Specific, evidence-based and recent. “We tested recovery of our order system from the isolated vault last quarter in six hours” is far stronger than “IT says we have backups.”
How executives can support recovery readiness
- Set clear risk tolerance for downtime and data loss
- Fund testing, not just technology
- Expect regular, evidence-based reporting
- Participate in at least one recovery exercise a year
Executive involvement turns recovery from an IT project into an organizational capability and makes it far more likely to work when it matters.
Key takeaways
- Cyber recovery is a board-level risk.
- Ask for evidence, not reassurance.
- Independent validation builds confidence.
Need an independent view for your board?
We provide board-ready, evidence-based assessments of recovery readiness.